
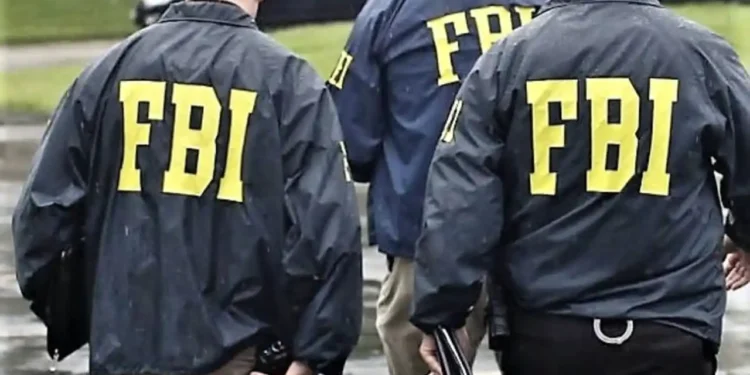
The United States Federal Bureau of Investigation, FBI, has launched an investigation into claims by a cyber-criminal group, ShinyHunters, that it breached the bureau’s systems and stole sensitive information belonging to about 38,000 employees.
The hacking group alleged that it gained access to extensive personal and professional information on FBI personnel, including names, job roles, badge numbers, residential addresses, telephone numbers and details about their spouses.
The FBI, however, has not confirmed that its systems were breached.
In a statement posted on X, the agency said it was aware of the claims and had commenced an investigation to establish whether its systems, or those of a third-party service provider, had been compromised.
“We are actively and aggressively investigating this matter and working closely with those third-party providers that support FBIJobs.gov to mitigate any and all risk,” the bureau said.
The claim emerged after ShinyHunters allegedly contacted journalists and began releasing samples and screenshots of the information it said was stolen from the FBI.
The BBC reported that it had reviewed a small portion of the alleged database and that some of the information appeared to be genuine.
Reuters also reported that some of the data allegedly contained details about officials’ job assignments, including work involving Chinese espionage, Russian intelligence and drug cartels.
If the full database is genuine, the breach could have serious implications for the safety and security of FBI personnel, particularly those involved in sensitive investigations and intelligence operations.
Former head of the United Kingdom’s National Cyber Security Centre, Professor Ciaran Martin, described the alleged breach as potentially one of the most serious forms of data compromise.
Martin said that, if confirmed, the incident would be “as serious as it gets when it comes to data breaches.”
Hackers claim access to multiple FBI systems
ShinyHunters claimed that it exploited a vulnerability in an Oracle cloud storage system used by the FBI to gain access to several systems containing sensitive information.
Among the systems allegedly affected are FBIJOBS, which handles recruitment-related information; FBI BEAST, reportedly used for background checks on employees and applicants; FBI MedLink, which contains medical information relating to agents; and FBI BICS, which holds investigation-related information.
The claims have not been independently verified by the FBI.
The group reportedly said it began its alleged attack on Monday night before contacting journalists on Tuesday with samples of the information.
Cyber-security experts have warned that even a partial compromise could expose FBI personnel to significant security risks, including identity theft, harassment, intimidation and potential targeting.
ShinyHunters demands FBI retract advisory
The group has also claimed that the alleged breach was not motivated by financial gain.
Instead, ShinyHunters reportedly gave the FBI one week to retract or amend a public advisory issued by the bureau in May that described the group as “threat actors.”
The FBI’s advisory accused ShinyHunters of using real or exaggerated claims of access to sensitive or personal information to pressure victims into making payments.
According to the advisory, the group has targeted major organisations in the technology, financial and retail sectors, allegedly stealing millions of customer records.
ShinyHunters said it was offended by the FBI’s description and threatened to publish the alleged FBI databases in full if the bureau failed to withdraw what it described as false allegations.
The FBI has not indicated whether it will comply with the demand.
Experts warn of possible retaliation
Cyber-security specialists have described the incident as an apparent retaliatory action against the FBI.
William Wright of Closed Door Security said the alleged attack demonstrated that major organisations remained vulnerable to cyber threats.
He said the group appeared determined to influence how its activities were perceived publicly and prevent statements that could damage its reputation.
Another cyber-security expert, Andrew Brandt of Huntress, said the decision to threaten a major US law-enforcement agency could expose the hackers to an intensified investigation.
According to Brandt, ShinyHunters would have to be confident that its members could avoid identification and prosecution before making such a threat against the FBI.
The bureau has not yet established whether the alleged hackers directly breached its internal systems or gained access through a third-party provider.
Its investigation is ongoing, while the authenticity and full extent of the information claimed by ShinyHunters remain subject to verification.
